
 AI Governance
 Data Centers
 Drones
 Climate
 Privacy
 2026 Maine Senate
 Bob Dylan

From AI Policies to Proof
Coverage from Bloomberg Law, Institute for Global Change, and others
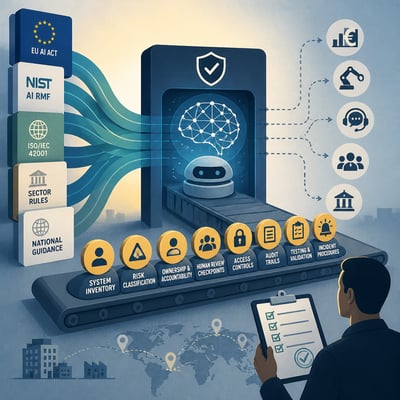
Organizations are formalizing AI oversight as systems move from experimentation into hiring, finance, customer service, software engineering, and other consequential activities.
The dominant shift is from policy documents to verifiable controls: inventories, risk classifications, named owners, human review, supplier oversight, continuous monitoring, and audit-ready evidence. The EU AI Act is an important global reference point, while NIST, ISO/IEC 42001, sector rules, and national frameworks shape implementation. The main unresolved challenge is extending accountability and control coverage to shadow AI, embedded vendor tools, autonomous agents, and systems that act through operational workflows.
The story broadens from agent-centric runtime governance to enterprise-wide control of informal, embedded, and autonomous AI used in consequential workflows. The main unresolved issue is now proving that documented controls operate effectively across shadow AI and vendor-integrated systems.
The story shifts from describing agentic governance requirements to showing runtime controls being operationalized as deployment infrastructure, particularly in financial institutions. Governance gaps are also framed more explicitly as lagging AI adoption.
The story shifts from designing governance controls to highlighting persistent visibility and accountability gaps around informal, embedded, and vendor-provided AI. It also adds clearer evidence of standards-body involvement and commercial tooling responses.
The story is largely confirmed, with a modest broadening toward vendor governance, third-party models and APIs, and software-development workflows. The current version also more explicitly distinguishes tested, enforceable controls from disclosure alone.
The update largely confirms the existing shift toward operational AI controls, while sharpening that automated governance cannot replace empowered human judgment in high-impact decisions.
The story is more explicitly reframed around runtime governance of AI agents, shifting accountability from model oversight toward controlling identities, permissions, tool calls, and downstream actions across fragmented regulatory regimes.
The story shifts from building AI governance structures to proving that controls work in practice. The central unresolved issue is now execution assurance, especially for shadow, embedded, and agentic AI.
The story shifts from designing governance frameworks to extending operational controls across overlooked AI use, technical workflows, and autonomous systems. Governance is increasingly framed as an operational and liability requirement, with fragmented implementation across jurisdictions complicating compliance.
Organizations are formalizing AI governance as AI systems and agents move into finance, engineering, customer operations, public-facing decisions, and other consequential workflows. The EU AI Act, NIST AI RMF, ISO/IEC 42001, sector rules, and national guidance are increasingly being translated into system inventories, risk classifications, named ownership, human-review checkpoints, access controls, audit trails, testing, and incident procedures. The main implementation challenge is making responsibility and evidence traceable when automated systems generate outputs, invoke tools, or take actions across organizational and supplier boundaries.