
 AI Governance
 Data Centers
 Drones
 Climate
 Privacy
 2026 Maine Senate
 Bob Dylan

AI Governance Briefing: Quick
Answering the key questions about the day.
AI Governance Advances Through Uneven, Partly Enforceable Layers
of Play
AI governance remains fragmented across jurisdictions and mechanisms. The EU retains active transparency and data-protection constraints while deferring major high-risk conformity duties; the United States has added a voluntary federal frontier-model review process while state-level targeted regulation continues to expand. In practice, organizations deploying consequential and agentic systems are increasingly relying on operational controls, but the decisive uncertainty is whether governments turn these emerging processes into enforceable, adequately resourced requirements.
What's New?
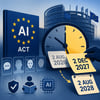
EU AI Act obligations are active but implementation is bifurcated
EU transparency duties are already enforceable, while the principal conformity obligations for standalone and product-embedded high-risk systems have moved to December 2027 and August 2028. GDPR restrictions on solely automated consequential decisions, including in hiring, remain in force, leaving important deployer constraints in place despite the AI Act delay.

US oversight remains a contested mix of voluntary federal action and state rules
Washington has a voluntary pre-release testing framework for powerful closed-source models, but its criteria, evaluator roles, and enforcement consequences remain unclear. In parallel, states continue to enact targeted rules on frontier models, chatbots, provenance, transparency, harmful uses, and consequential decisions; no comprehensive federal regime has displaced this patchwork.
Governance is increasingly being built into deployment operations
Large healthcare deployments and enterprise-agent guidance point toward centralized inventories, evaluation and monitoring workflows, distinct agent identities, scoped permissions, logging, and shutdown or rollback capabilities. These are emerging institutional practices rather than a harmonized legal or technical baseline.
- centralized inventories
- evaluation and monitoring workflows
- distinct agent identities
- scoped permissions
- logging and shutdown or rollback capabilities
What's Changed?
Federal frontier-model review has moved from debate to a voluntary framework
The White House's August framework introduces pre-release testing and a 30-day government safety and cybersecurity review for powerful closed-source models. This modestly advances federal operational involvement from the prior politically unsettled baseline, but does not yet establish published thresholds, a clearly accountable evaluator, mandatory participation, or intervention powers.
- pre-release testing
- a 30-day government safety and cybersecurity review
- published thresholds
- a clearly accountable evaluator
- mandatory participation
- intervention powers
The framework modestly advances federal operational involvement but does not yet establish enforceable oversight.
State-level targeted regulation has become more clearly consequential
Newly consolidated reporting shows continued enactment and revision across California, Texas, Colorado, Connecticut, Utah, and Washington. The meaningful update is not a single comprehensive state framework, but stronger evidence that state rules remain the practical source of many US AI obligations while federal preemption and federal oversight remain unresolved.
What Matters?
The EU delay shifts the near-term governance burden to existing law and narrower AI Act duties
Deferring high-risk conformity obligations extends the period in which broad ex ante AI Act controls are incomplete. Yet enforceable transparency duties and GDPR-based limits on consequential automated decisions preserve meaningful constraints, producing uneven protection across use cases rather than a general regulatory pause.
US preemption without enforceable federal substitutes would widen the accountability gap
The federal voluntary review framework may create a common process for some frontier developers, but its unresolved governance architecture contrasts with the concrete targeted obligations emerging in states. Whether federal policy supplements or displaces those rules will determine whether US governance converges around enforceable safeguards or becomes less accountable in the name of uniformity.
Whether federal policy supplements or displaces state rules
Operational controls are becoming the immediate governance layer for agentic deployment
As agents gain access to data, records, tools, and other agents, accountability increasingly depends on runtime controls rather than high-level principles alone. The emerging practices can reduce operational risk and create audit evidence, but reported adoption remains limited and does not substitute for consistent external standards or supervision.
What's Next?
Watch whether EU authorities use transition-period powers before high-risk deadlines
Evidence that the AI Office or national authorities demand information, require corrective measures, restrict deployments, or impose penalties under already-active duties would show whether practical discipline is developing despite deferred high-risk conformity requirements. Continued absence of such action would reinforce the implementation gap.
Whether practical discipline develops during the transition period
Watch for enforceable design of the US federal review regime
Publication of model thresholds, testing criteria, evaluator assignments, participation requirements, reporting duties, or authority to require safeguards or delay deployment would demonstrate movement from voluntary process to operational federal oversight. Preemption initiatives without comparable duties would instead strengthen the accountability-gap assessment.
Whether the US federal review regime becomes enforceable
Watch for sectoral requirements that convert enterprise controls into de facto regulation
Binding supervisory or procurement requirements for model-release controls, agent authorization, third-party resilience, incident response, and recovery testing—particularly in finance and healthcare—would indicate that sectoral governance is compensating for gaps in comprehensive frontier oversight.
- model-release controls
- agent authorization
- third-party resilience
- incident response
- recovery testing