
 AI Governance
 Data Centers
 Drones
 Climate
 Privacy
 2026 Maine Senate
 Bob Dylan

macOS Infostealers Exploit Fake Prompts
Coverage from BleepingComputer and others
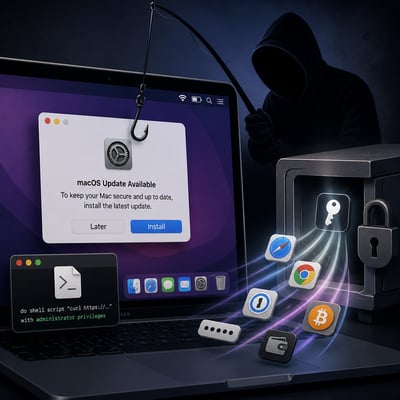
Multiple macOS infostealer campaigns are using fake Apple or security prompts, ClickFix-style lures, and trusted tools such as Terminal and Script Editor to persuade users to run malware or disclose their passwords.
The malware targets Keychain credentials, browser data, password managers, files, and cryptocurrency wallets, with some variants adding persistence and remote-control capabilities. The activity shows a consistent shift toward social engineering and abuse of legitimate macOS workflows rather than reliance on software exploits alone.
The story is now framed more tightly around fake macOS system prompts and trusted built-in tools as the main delivery mechanism, with less emphasis on specific malware names and more on the breadth of credential theft and persistence techniques. The current version also adds that some variants go beyond theft by loading payloads or opening reverse shells.
The story broadens from a general macOS infostealer pattern into a more specific, multi-family campaign set with clearer delivery methods, persistence behavior, and one quantified impact report. The current version also adds several named actors and strengthens the case that these operations combine credential theft with durable remote access.