
 AI Governance
 Data Centers
 Drones
 Climate
 Privacy
 2026 Maine Senate
 Bob Dylan

Hackers Target Microsoft 365 Credentials
Coverage from BleepingComputer, Krebs on Security, and others
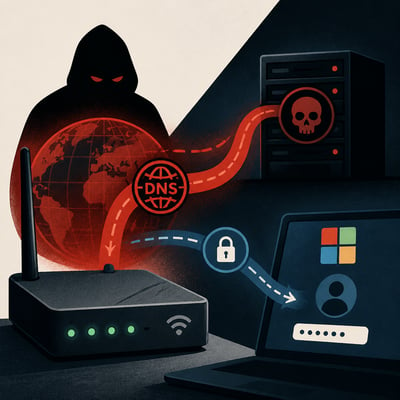
Threat actors are targeting Microsoft 365 identities through two complementary paths: APT28 has redirected authentication traffic by compromising vulnerable SOHO routers, while a separate campaign used exposed credentials and the Azure CLI to conduct large-scale password spraying.
The activity shows how attackers can obtain account access or tokens by exploiting weak edge-device security, legacy authentication flows, incomplete MFA policies, and reused credentials. Law-enforcement disruption has removed some infrastructure, but affected organizations and users still need to patch or replace exposed routers and strengthen identity controls.
The update adds a clearer operational detail on the router-hijacking side and expands the response story: the APT28 campaign is now tied to a named operation and confirmed disruption by additional authorities, while remediation is framed as still incomplete. The separate password-spraying campaign is largely unchanged.
The story broadened from a single APT28 router-hijacking operation into a wider set of Microsoft 365 credential attacks, including a separate large-scale password-spraying campaign that succeeded despite MFA gaps. It also adds more precise scale, timing, and affected-organization details, making the identity-policy weaknesses more prominent.